
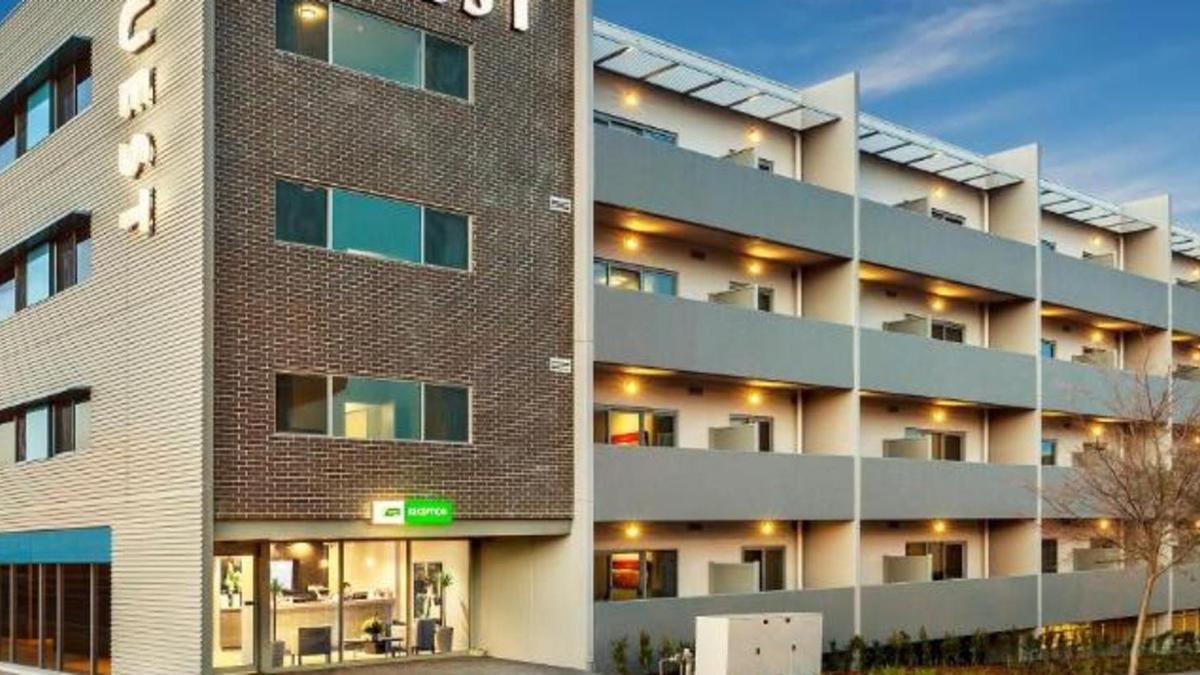
More than 1.9 million Quest Apartment Hotels customers have been affected by a data breach in which passport and driver’s licence numbers were accessed, along with other sensitive personal information.
The hotel chain discovered unauthorised access to a database linked to a third-party technology provider on August 17. Forensic analysis found the affected records dated from before June 2025.
Quest initially said names, addresses, telephone numbers and email addresses had been compromised. Further analysis identified more than 225,000 vehicle registration details and over 104,000 passport and driver’s licence numbers among the accessed data.
More than 297,000 credit card details were also involved, including over 46,700 records containing a card’s CVV number. Birth dates, NDIS numbers and Medicare numbers were also caught up in the breach.
The Ascott Limited managing director, David Mansfield, apologised to customers and said the company was supporting those affected.
“We know that people trust Quest with their personal information when they choose to stay with us. We do not take that responsibility lightly,” he said.
“We remain focused on supporting affected individuals and on continuing our review of the measures used to protect information entrusted to us.”
Advice for customers affected by the Quest data breach
Quest is contacting customers whose information was involved. Anyone whose driver’s licence number was compromised has been advised to contact the authorities to find out what steps they should take.
Customers have also been assured that robust controls were in place to protect passport information from identity takeover.
Kash Sharma, managing director of cybersecurity company BlueVoyant, said the breach would affect many Australians because Quest was a trusted brand. He warned that hospitality businesses held large volumes of personal information that could not simply be reset once exposed.
“The immediate risk for affected customers isn’t the breached data on its own, it’s what attackers do with it next,” he said.
“Names, contact details and dates of birth are the raw ingredients for convincing phishing and identity fraud, including fake emails that look like they come from Quest itself.”
Mr Sharma urged customers to be cautious of unexpected messages about bookings, refunds or account verification, and to avoid clicking on links or attachments. He said people should contact the company through official channels if they needed to check information.
He said the incident also highlighted the risks posed by third-party technology providers, arguing that organisations handling customer data needed to maintain visibility of which suppliers could access it and how securely it was being managed.
