
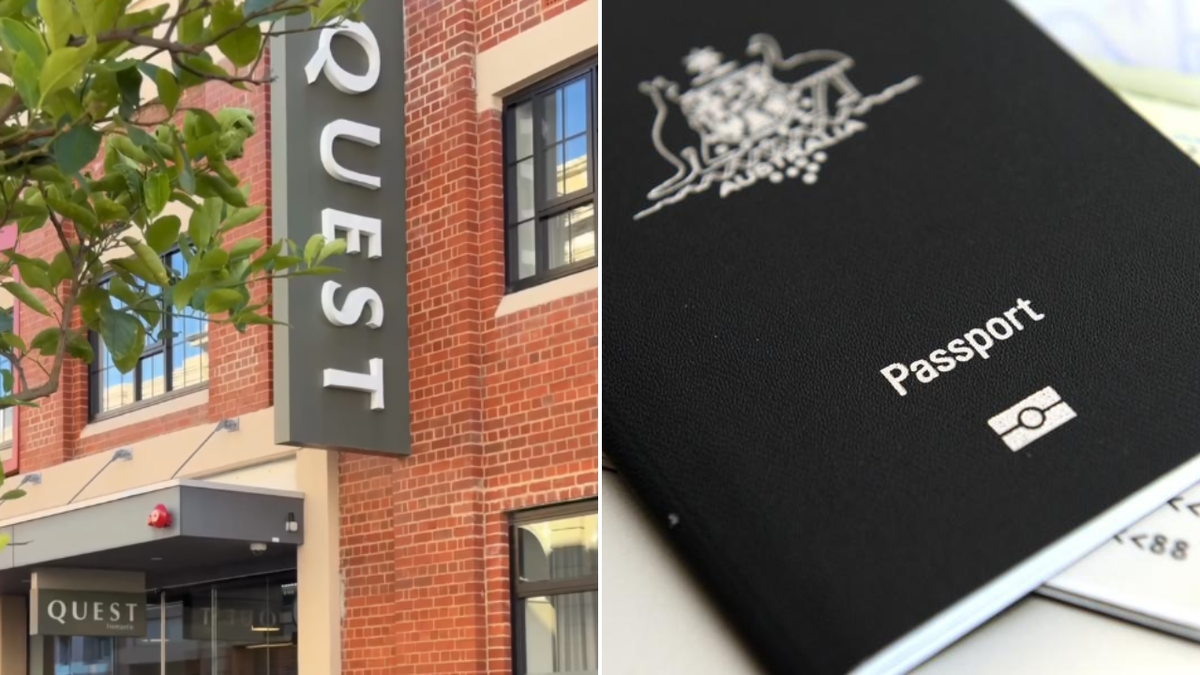
Quest Apartments customers have been urged to check with the relevant authorities after an investigation into a major data breach found that passport and driver’s licence numbers had been compromised.
The accommodation provider said information relating to 1,991,613 customers was affected in the incident, which was first disclosed in August.
Quest initially said the breach involved information dating from before June 2025, including names, email addresses and other contact details. Further forensic analysis has now identified passport and driver’s licence numbers, credit card numbers including CVV details, and other personal information among the data exposed.
Quest said 104,268 records containing a passport number, a driver’s licence number or both were affected. It stressed that scanned copies of the identity documents were not compromised.
In messages sent to affected customers, the company advised people whose driver’s licence numbers were involved to consider contacting their local road authority about obtaining a replacement licence.
Those whose passport numbers were affected were told to contact the Australian Passport Office, or the relevant issuing authority for non-Australian passports, to discuss whether their passport should be flagged or reissued.
Quest later said the advice had always been for customers to check with the relevant issuing authorities as a precaution. It also directed customers to guidance from the Australian Passport Office stating that passports affected by the breach did not need to be replaced.
The company said it was continuing to work with the relevant authorities to keep customers affected by the third-party supplier data breach informed.
David Mansfield, managing director of Quest operator The Ascott Limited Australasia, apologised to those affected.
“For the overwhelming majority of impacted individuals, the information identified at that preliminary stage was limited to a combination of name and contact information,” he said.
“Our forensic data analysis has now enabled us to determine the specific types of personal information affected.”
“I recognise the concern this incident has caused. On behalf of Quest, I sincerely apologise to those who have been affected.”
